- ShinyHunters claims it stole up to 3 terabytes of sensitive data on thousands of FBI agents, applicants and their families.
- The group says the attack was retaliation for an FBI advisory that called their threats exaggerated and urged victims not to pay.
- The FBI says it is “actively and aggressively” investigating but has not confirmed what was taken or where the breach occurred.
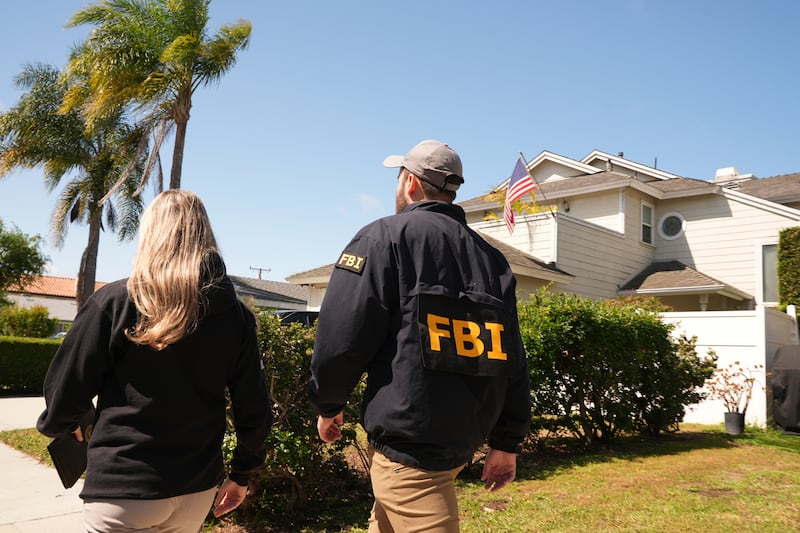
The FBI is investigating claims that hackers breached its online job portal and stole sensitive information for thousands of current and former bureau employees, potentially exposing agents and their families to fraud, harassment and foreign intelligence threats.
The hacking group ShinyHunters claims it attacked the FBI in retribution for a statement the agency released earlier this year describing its tactics as “exaggerated” and urging victims not to pay them. ShinyHunters has not yet leaked the stolen data, but is demanding that the FBI correct or remove the statement within one week of the attack or face further consequences.
The FBI is “actively and aggressively” investigating the claim and working to identify whether the breach was through a third-party or the FBI’s actual enterprise.
Inside the alleged breach
If the hacking group’s claims are true, the FBI job portal acted as the front door that gave ShinyHunters a path to far more data than just job applications.
The job portal runs on Oracle’s PeopleSoft software, which processes and stores all the applications and employee human-resources records. This includes names, home addresses, phone numbers, dates of birth, Social Security numbers, and spouse and emergency-contact details.
ShinyHunters claims it found a previously unknown flaw, called a “zero day exploit,” in the PeopleSoft software and used it to break into the jobs portal on Monday night. Once inside, the group copied between 2 and 3 terabytes of files containing hundreds of millions of pages of records.
“We have compromised the FBI,” ShinyHunters posted online. “We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job.”
The day after the alleged attack, the job portal homepage displayed a banner that read, “THIS SITE HAS BEEN SEIZED BY SHINYHUNTERS.” The hacking group also disclosed what it claims to be a sample of the stolen information to several news organizations.
When checked against publicly available information, some of the sample data appeared to match real individuals, suggesting the data could be authentic.
“The FBI is aware of a cybercriminal enterprise group claiming a compromise of the fbijobs.gov portal. ... We are actively and aggressively investigating this matter and working closely with those third-party providers that support fbijobs.gov to mitigate any and all risk,” the FBI released in an official statement.
Reuters reported that some of the materials went beyond personal information, revealing details about agents’ sensitive work assignments such as classified counterintelligence operations and investigations into drug cartels.
What is at stake
If confirmed, the breach carries implications far beyond identity theft or extortion.
Other cybercriminal groups similar to ShinyHunters have historically used hacked data to target and intimidate FBI agents investigating their illegal activities. Additionally, leaked personal information could give convicted criminals a way to find and retaliate against the agents who arrested them.
“What worries me most is how any criminal with a grudge could use this data to target and physically harm not only the FBI agents who investigated them, but also those agents’ families,” said Cynthia Kaiser, a former FBI cybersecurity official, according to The New York Times.
The data could also be dangerously beneficial for foreign intelligence agencies, particularly those looking to understand how the FBI operates and who its people are. If posted on the dark web, hostile governments could use agents’ personal details to identify, track or recruit against them.
A history of extortion
ShinyHunters has been active since 2019 and has typically targeted major tech, finance and retail companies for financial gain.
In 2024, ShinyHunters hacked AT&T and stole data on 110 million customers, exacting a $370,000 ransom before deleting the information. That same year, they stole 560 million users’ records from Ticketmaster and demanded $8 million in return.
Just months before the FBI hack, ShinyHunters stole 3.65 terabytes of data from 275 million users across 9,000 schools by hacking Instructure, the company behind the educational platform Canvas. ShinyHunters injected ransom demands into hundreds of school login pages during final exams, which forced Canvas offline until Instructure paid the ransom.
A battle for credibility
ShinyHunters claims that unlike previous attacks, the FBI breach is not motivated by money. In the group’s post announcing the attack, ShinyHunters wrote that the hack is not a ransom or extortion and “is NOT financially motivated.”
The hacking group claims that the attack is in retaliation for a statement the FBI released after the Instructure breach earlier this year. The public service announcement describes ShinyHunters as a criminal extortion group that exaggerates or even fabricates its claims to pressure victims into paying, and advises individuals not to comply.
The statement infuriated ShinyHunters because it strikes at its credibility, which is the one thing the entire hacking business depends on.
“We wish to state unequivocally our threats and claims are very real. Not exaggerated and never a bluff,” ShinyHunters said in its initial post announcing the attack. “As a big believer and supporter of the U.S. Constitution — we are exercising the First Amendment and actively combating disinformation.”
The FBI continues to investigate the legitimacy of the attacks and the sensitivity of any stolen data. Jason Pack, a retired FBI special agent and current CEO of Media Rep Global Strategies, told Fox News that there is an important distinction between a personnel data breach and full access to classified systems.
“There is a meaningful difference between somebody obtaining personnel information and somebody gaining access to classified investigative systems,” Pack said. “Based on what we know right now, there is no indication they have the keys to the kingdom.”